Real attacks. Real lessons.

OT, automotive and product cybersecurity analysis.

See what real incidents mean for your engineering decisions. Read the case studies, listen to the podcast or use free worksheets to prepare your next review.

For engineers and security teams working on industrial systems, connected vehicles and digital products.

Prefer a weekly briefing?

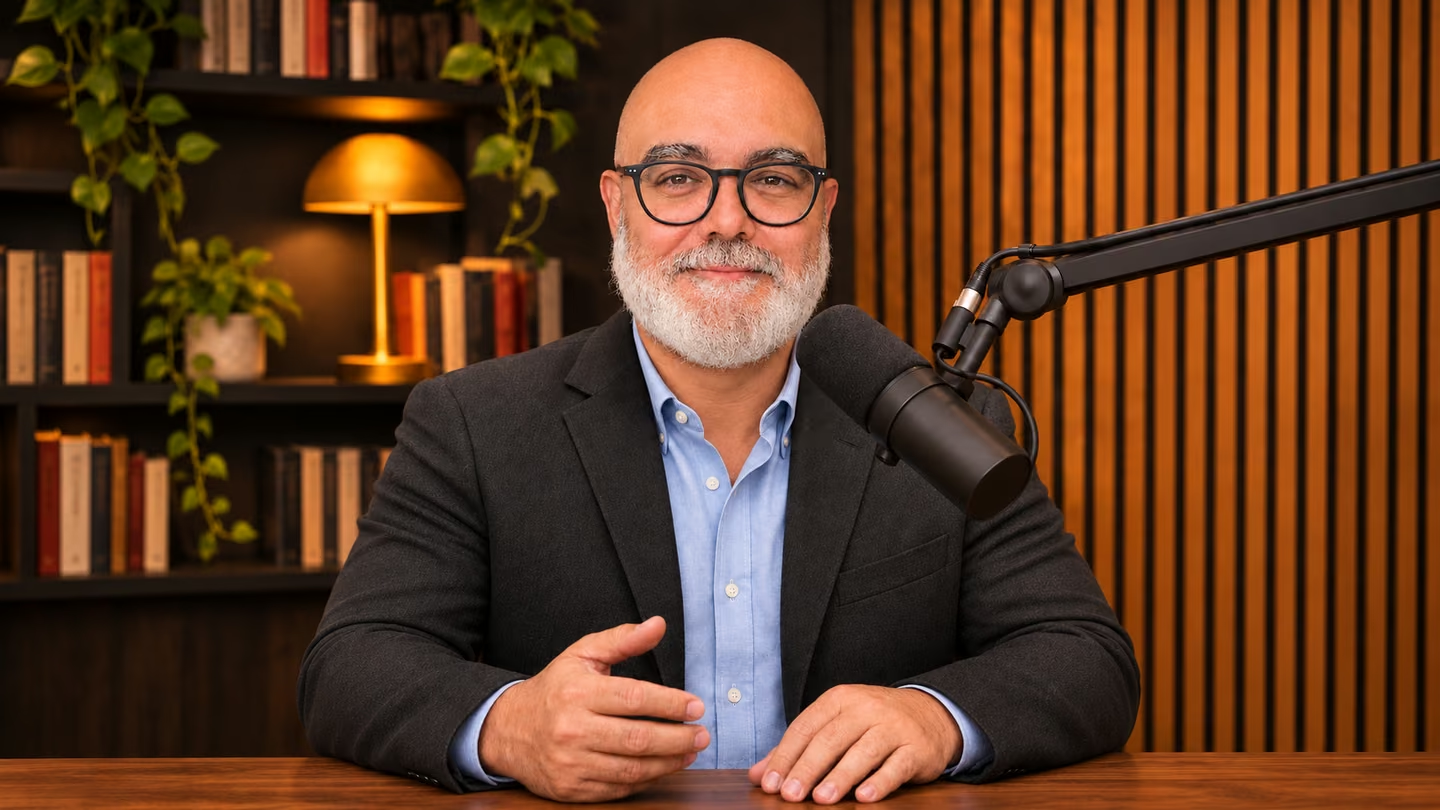
Antonio González in the Cybersecurity Under Pressure studio
Antonio González, PhD · Founder & Editor
Featured analysisOT & ICS · Mitigation Assurance · 1 source ↗

The Patch Is Deferred. Is the Compensating Firewall Rule Still There?

A deferred patch depends on controls that survive maintenance and fault recovery. Monitor relevant configuration changes and permitted paths, then reopen the operating decision when its assumptions fail.

Read analysis →

The decision

An authorised exception should identify its purpose, duration and compensating arrangements. Determine whether diagnosis can continue with narrower access or whether the vulnerability requires earlier intervention. If no supported temporary measure remains, escalate the operating restriction instead of leaving the original acceptance unchanged.

Explore the library

Start with your system or your decision.

Choose an operating context, or follow an assurance question across sectors.

Need to review a real decision? Choose from six free evidence worksheets →
OT access · SBOM/VEX · Automotive · IEC 62443 · CRA · AI Act

New to CUP? Start here →
Latest analysis

Signals worth keeping.

All analysis →
Automotive · Diagnostic Security

The UDS Routine Works. Does It Refuse the Wrong Vehicle State?

RoutineControl acceptance needs both the diagnostic response and the actual routine behaviour, including loss or staleness of the signals used to decide whether execution is allowed.

Read analysis →
Railway · Maintenance Security

A Railway Maintenance Credential Meets a Safety Case and a Change Quote

Replacing a shared maintenance credential becomes an engineering and commercial decision when compatibility evidence and safety assessment sit with a subsystem supplier.

Read analysis →
IT · Edge Infrastructure

NetScaler: patch the device, prove the service

A fixed build closes the known vulnerability. A controlled service check shows whether authorised users can still reach the application after failover.

Read analysis →
Automotive · Vulnerability Management

When Is a Supplier’s VEX Assessment Enough to Avoid an ECU Update?

A not-affected statement must identify the product and explain its technical basis. Product-intrinsic exclusion, configuration assumptions and external containment support different decisions.

Read analysis →
From the archive · OT & ICS

The Restart Bottleneck Is Not the Backup. It Is the Evidence.

Read analysis →
From the archive · Railway

When a Security Patch Collides with the Safety Case

Read analysis →
The podcast

One case.
More room
to reason.

Read the evidence and technical implications, or take the same case into the podcast for a deeper discussion of trade-offs and decisions.

Browse episodes
01
11 Nov · 32 min

PLC Logic Changes During Live Production: An OT Pressure Test

  • Keep possible change paths separate from confirmed observations.
  • Correlate the authorisation record with evidence from the controller and engineering path.
  • Agree operational authority for continuing, isolating or stopping before an incident.
→
03
14 Oct · 33 min

The Integrator Is Part of the OT Trust Boundary

  • A secure tunnel does not constrain what an authenticated third party can change.
  • Integrator identities should be named, time-bounded, least-privileged and reconstructable after an incident.
  • Customer engineering data held by suppliers is part of the downstream attack surface.
→
Free tools & worksheets

One review. A practical action plan.

Choose the decision in front of you. Identify missing evidence, assign owners and export a report to take into your next review.

Compare all six worksheets →

A supplier needs access to your plant.

OT remote access →

Review one supplier connection: who can connect, what they can change, when access ends and who can stop it.

You need to assess a vulnerability claim.

SBOM & VEX assurance →

Challenge one product-component-vulnerability claim and record the evidence, response owner and unresolved actions.

A vehicle change or update needs a review.

Automotive cybersecurity & updates →

Review one vehicle change or software update across engineering evidence, supplier responsibilities and the release decision.

You need evidence for an industrial system.

IEC 62443 system assurance →

Connect an industrial system boundary, accountable roles and implementation evidence to the operational acceptance decision.

You are preparing a product for CRA review.

CRA product readiness →

Scope one product and market activity, then review product security, vulnerability handling and reporting-readiness evidence.

An AI use case needs a deployment decision.

AI Act use-case review →

Define one AI use case, your role and the applicable pathway, then identify evidence gaps before a deployment decision.

Free · No account required · Fictional examples included. Entries stay in your browser; use non-sensitive references only. These tools organise evidence and actions; they do not certify compliance.

Looking for a comparison of the frameworks? Open the separate R155 & IEC 62443 evidence map →

The Weekly Brief

Three real incidents. The engineering consequence. The decision that matters.

About five minutes, once a week. For OT, product security, automotive, railway and critical-infrastructure professionals who need evidence and decisions, not another alert stream.